AYITA
The governed runtime for regulated AI work.
AI agents and people work inside enforced policy. Consequential actions are checked before they happen - and every decision leaves an audit-grade trace.
Why enterprise AI resists control
Most AI systems don’t expose what they know, how they decide, or where your data goes. Control breaks long before governance, audits, or compliance come into play.
Memory is a black box
You can’t see what the AI remembers, what it retains, or why.
Responses aren’t reproducible
The same question can produce different answers, with no way to recompute or verify them.
Decisions leave no trail
There is no audit-grade trace explaining how a result was produced.
Data crosses boundaries
Context, embeddings, or inferred knowledge leak outside your perimeter.
What is AYITA?
AYITA is the governed workbench where AI agents and people work inside enforced policy. Every consequential action is checked before it happens, named humans stay in the work at the moments that matter, and every decision is recorded as audit-grade evidence.
Editable memory
You define what the AI can retain, reuse, or forget - and correct what it already knows. Full control, not just visibility.
Deterministic behavior
The same case and policy produce the same verdict. Every governed decision can be independently recomputed and verified.
Decision traceability
Every decision is logged with full lineage. What happened and why is always explainable.
Controlled boundaries
Data, context, and inference stay inside your environment. No uncontrolled data movement.
Somewhere between agent one and agent fifty, oversight stops being a team process and becomes an architecture problem.
Bespoke, sandboxed agent deployments work while a small team still holds the whole picture. They stop working when the count grows.
Agents get built in weeks and validated in months. The bottleneck isn't the model - it's the approval.
The engineering is not what holds the deployment. The sign-off is.
Govern actions before they happen.
The model can reason freely. AYITA governs the consequential actions - tool calls, data access, external sends, approvals, and decisions - before they happen.
How AYITA is different
Most "AI governance" either watches or assists. AYITA governs the action itself. Here is how it compares to the usual approaches.
vs Chatbot guardrails
Guardrails filter words. They cannot stop a tool call, a data send, or an approval - and leave no evidence.
vs Governance dashboard
A dashboard reports after the fact. Seeing a problem is not the same as preventing it.
vs Copilot / assistant
Copilots optimize for speed, not approval - no enforced policy on actions, no audit trail.
vs Platform agent gateways
Gateways govern access - who may call what. They do not adjudicate the action itself, and they run on the platform's cloud.
None of this is rip-and-replace. Classification and visibility tools keep their jobs - AYITA is the enforcement point beside them.
Architecture, not just guardrails
Most governance tools watch the model from the outside. AYITA's governance is built into the runtime itself - which is what makes its verdicts explainable and its evidence reproducible.
Model-is-a-Plugin
Inference is swappable. Bring your own model - Anthropic, open-weight, or on-prem - and the governance layer stays the same. You are not locked to one vendor's model, and switching models never weakens your controls.
MARM - governed memory
Memory is not an opaque vector store. MARM gives agents a governed memory scaffold with consistent metadata and relations, so what an agent retains, reuses, or forgets stays inspectable and policy-bound over long-running work.
ATE - deterministic trust engine
Verdicts come from a deterministic, Bayesian trust engine with zero LLM calls in the verdict path. The same case and policy produce the same verdict - byte for byte, every time.
Cryptographic agent identity
Every agent carries a cryptographic identity, and every delegation between agents is a signed chain - scoped, time-bound, revocable, and auditable. When a reviewer asks which agent acted and under whose authority, the answer is provable rather than inferred from logs.
Your agents, governed
AYITA governs the agents you already run - it does not ask you to rebuild them. Existing agents and stacks connect by configuration, not re-architecture, and keep doing their work inside enforced policy. Planning, delegation and execution control (NODIN) ships inside AYITA.
Per-role, per-context policy
Policy is not one global setting. What an agent may do, what memory it may reach, and which actions need a named approver are configured per role and per context - so an analyst in one jurisdiction and a reviewer in another operate under different enforced rules on the same deployment.
The trust engine, in detail
ATE is the deterministic core of the runtime. It is where a policy stops being a document and becomes a decision the system makes before the action takes effect.
It decides, it does not recommend
ATE sits in the pipeline as an execution gate, before the action - not beside it as advice. Dashboard governance never sits here; it reports on what already happened.
Zero LLM calls in the verdict path, by construction
No model is consulted to reach a verdict. That is an architectural property, not a configuration - and it is why the verdict path can be certified where LLM-based trust scoring cannot.
Same case, same policy, byte-identical verdict
Every decision emits a BeliefSnapshot - an audit-grade record of which conditions were checked and why the decision came out the way it did. A reviewer recomputes it and gets the same answer.
Contradictory-policy resolution
Regulated environments run on policies that contradict each other across versions and jurisdictions. The engine resolves precedence and returns go / no-go with an explainable reason - rather than escalating the conflict to a human to untangle.
Policy as rules
A regulation or an internal policy decomposes into rules and loads into the engine. A new regulation drops in without re-engineering the runtime around it.
Stateful trust
Trust carries across a workflow: a budget depleted at step 4 changes the verdict at step 5. And the engine demonstrably approves as well as blocks - it is a decision engine, not a brake.
Where it runs
Realm does not sell you compute. The runtime, the models and the evidence all stay where your data already is.
In-perimeter inference
Realm ships with an in-perimeter inference server, deployed inside your environment.
Your models, your ground
Models - including the institution's own - run inside the institution's environment.
Hyperscaler optional
External inference endpoints can be used, and are never required.
Connects by configuration, not re-architecture - your existing agents and stack stay.
How AYITA works
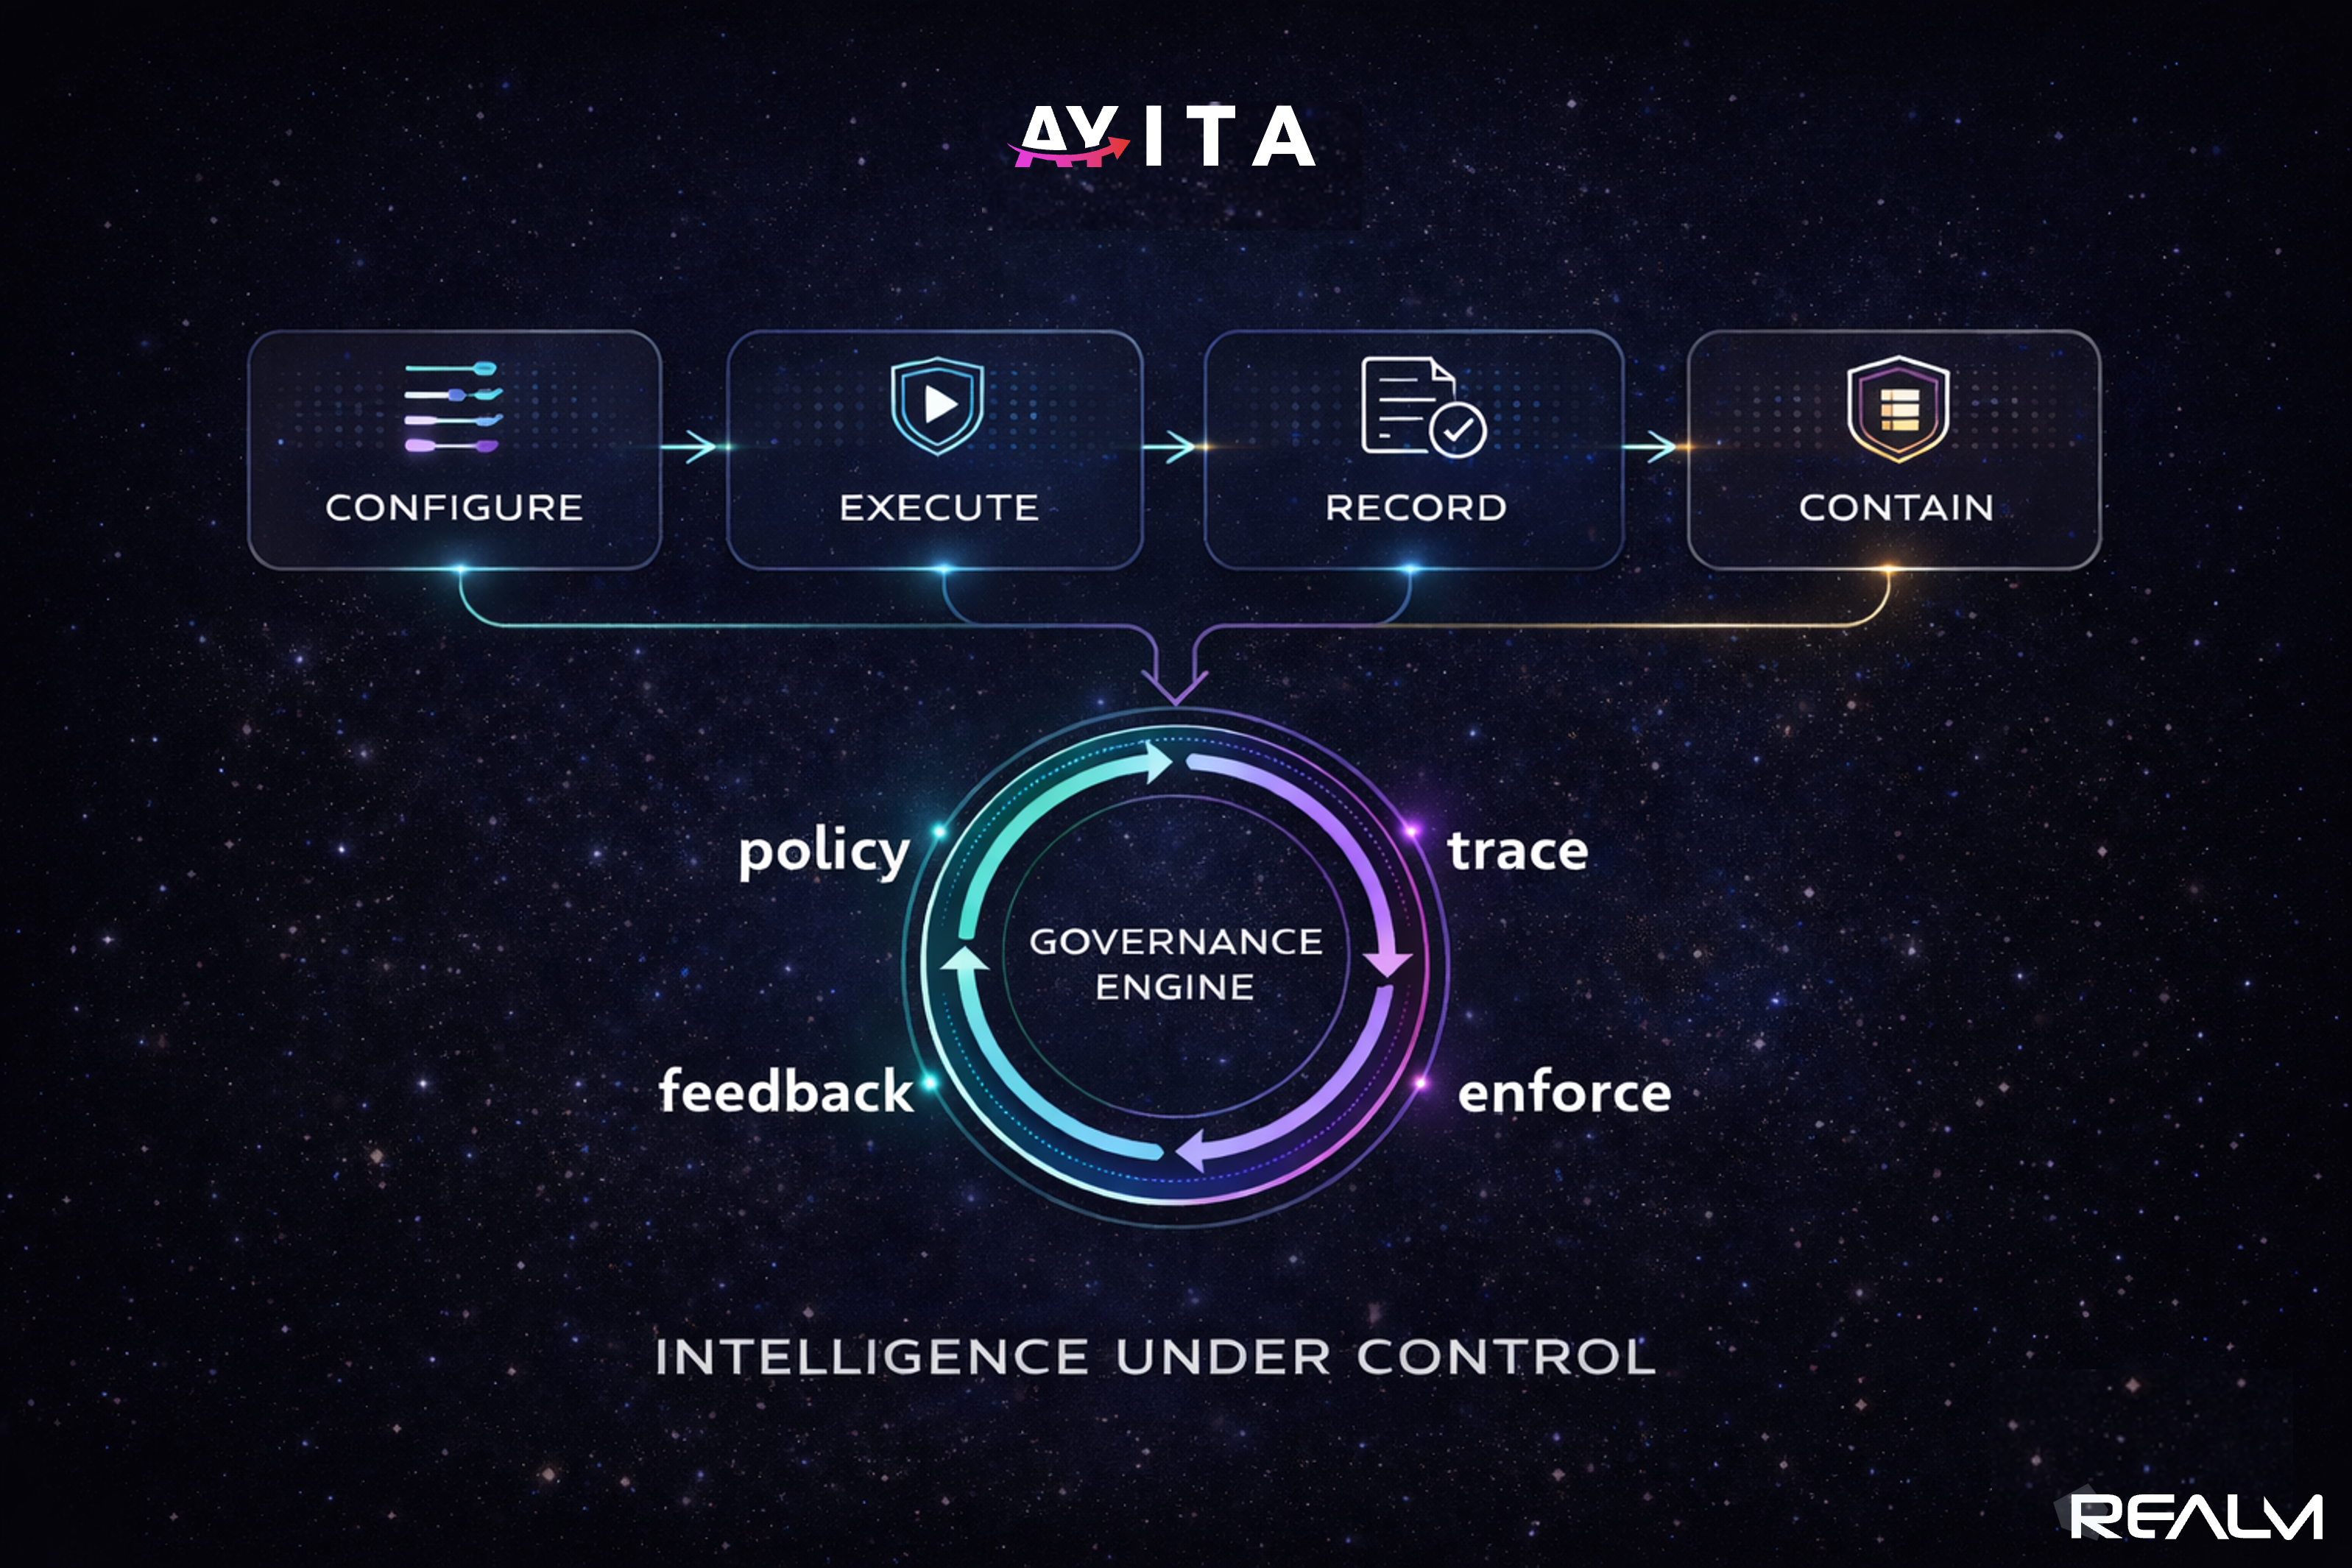
AYITA applies control as a continuous process. Policies are configured upfront, enforced at runtime, and verified through complete execution records.
-
→
Configure
Define policies, memory rules, and data boundaries before any AI execution begins. -
→
Execute
Run AI workflows inside a controlled runtime. The same inputs reliably produce the same outputs. -
→
Record
Log every step with full lineage. Inputs, prompts, outputs, and controls are captured. -
→
Contain
Keep data, context, and inference inside your perimeter. No uncontrolled data movement.
What AYITA produces as evidence
Every AYITA execution produces concrete artifacts. AI behavior becomes reviewable, testable, and provable.
Recomputable execution records
Complete records that let any governed action be recomputed step by step - the policy state, what the model received, what the human saw.
Memory state snapshots
Timestamped snapshots of what the AI retained, reused, or discarded.
Decision trace records
Structured traces linking inputs, policies, decisions, and outputs.
Perimeter boundary reports
Evidence that data, context, and inference remained inside approved environments.
Human-in-the-loop is not enough for regulated AI.
A person approving a summary at the end is not real oversight. AYITA keeps named humans in the work at the moments that matter - seeing the actual case, decision, and evidence before approval.
Human-in-the-loop
Approval at the end of the workflow, on a summary - after the action has already happened.
Human-in-the-work
Named people start and drive the work alongside the agents, and named reviewers act at the consequential moment - on the actual case and evidence, before the action is allowed.
The named person is not only a checkpoint. A workflow in AYITA has participants - a person initiates the case and drives it, agents carry the work under enforced policy, and named reviewers clear the consequential steps. Every participant, human or agent, is identified in the record.
AYITA in regulated AI work
Three moments where AYITA governs the action before it happens.
Sensitive data send
An AI agent tries to send customer records outside the company. AYITA checks the outbound action before it happens, blocks or escalates it, and records the decision.
Gate: external send blockedDecision approval
A reviewer cannot approve a regulated decision from a summary alone. AYITA requires the reviewer to see the actual case and records what was reviewed and approved.
Gate: human approval requiredLong-running agent drift
An agent working on a long task starts drifting from the original goal. AYITA keeps the workflow traceable through governed memory, policy checks, and evidence capture.
Gate: policy check on every stepWhat an AYITA Cognitive Trace Pack shows
"Audit-grade evidence" should be something you can hold. Every governed action produces a Cognitive Trace Pack - a structured record of what happened and why.
AYITA is to commodity LLM inference what Snowflake was to commodity storage: the governed layer that turns a raw capability into something a regulated enterprise can actually run on.
- Who actednamed user
- Which agent actedagent + version
- What was requestedaction + payload
- What policy appliedrule + version
- Verdictapproved / blocked / escalated
- Which human reviewedreviewer + time
- Evidence capturedtrace + memory state
Continuous evidence, not a point-in-time approval
What an oversight or security-operations function needs is not a certificate. It is a signal that keeps arriving.
The approval snapshot
A project is signed off, a certificate is filed - and the record is frozen on the day it was granted while the system keeps changing underneath it.
The production stream
Every governed action emits a trace in production - a stream the team can watch, alert on, and investigate while the work is happening, not a quarter later.
And the signal stays evidence. Any verdict in that stream can be recomputed offline weeks later, from the same inputs and the same policy version, and produce the same result.
See AYITA at the Moment of Decision
Agents and people act. AYITA decides what is allowed - deterministically, and records it. (See the Healthcare tab for agent gates.)
Compliance Manager
AML / KYC / Treasury
AYITA does not replace professionals.
AYITA appears at the moment of responsibility.